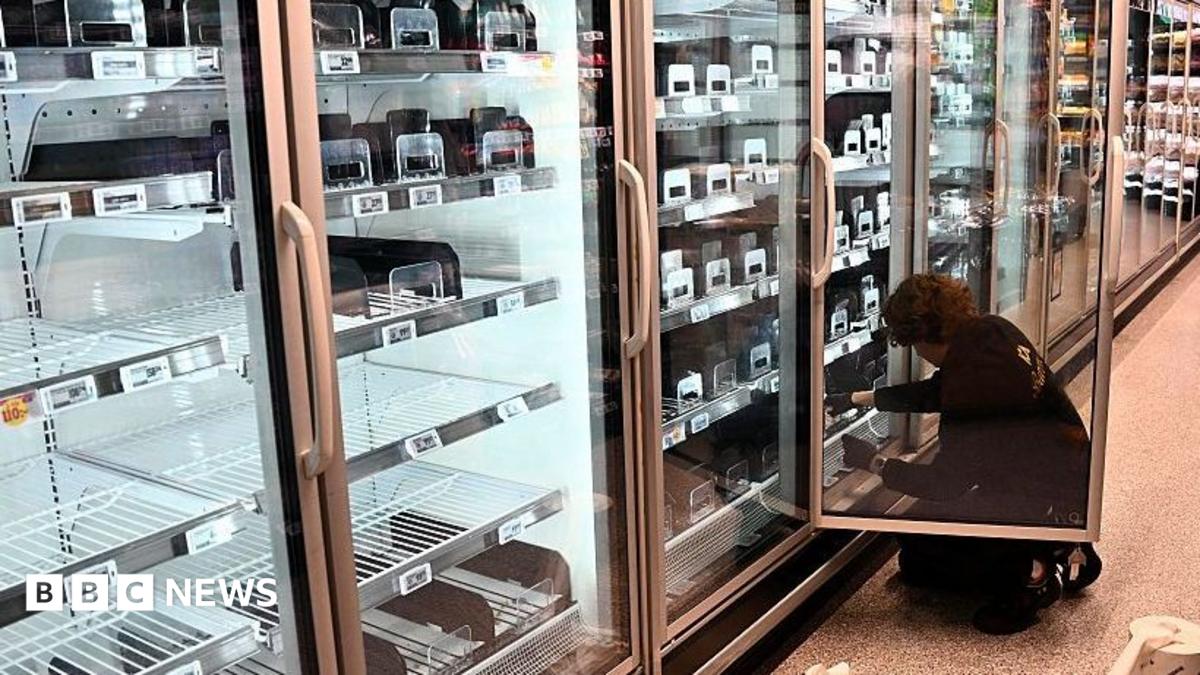
French authorities say that fridges utilized in medical amenities to retailer blood for donations have been impacted by latest cyber-attacks by unknown hackers.
The French Blood Institution (EFS) mentioned chilly rooms storing blood have been impacted by hackers, with temperatures set to rise – however employees intervened to guard blood provides.
“No well being impression has been recognized and no lack of blood merchandise is to be reported,” the EFS mentioned.
Up till now, solely supermarkets have been identified to have been impacted by the hacks.
In the meantime rumours have been circulating on-line about Russian hacktivist teams claiming they labored collectively to hack one of many programs that was used within the assaults which have affected European supermarkets.
Noname057(16) and Z-Pentest Alliance posted that they efficiently hacked Danfoss which led to hypothesis that they have been the culprits behind the freezer hacks.
However analysts now query whether or not or not that meant they have been behind the grocery store cyber-attacks.
Whereas Russian teams should not being dominated out, specialists say Iranian hacktivists or nation state hackers – and even youngsters pulling pranks – may be the culprits.
Cyber-security researchers at a number of companies are poring over proof gathered from so-called “honeypots” to offer clues as to who’s behind the waves of freezer hacks.
Three separate cyber-security companies have deployed faux freezer software program traps to observe how hackers try to make use of them for assaults.
In cyber-security, a “honeypot” is a digital decoy – comparable to a faux pc community or file – intentionally set as much as appear like a weak goal to lure and entice hackers.
By monitoring these traps, safety specialists can safely research an attacker’s strategies with out placing actual programs in danger.
In accordance with exercise gathered after the primary wave of cyber-attacks, the second wave which hit a number of European nations was extremely focused.
“The truth that all these fridge freezers have been hit concurrently suggests planning and coordination,” says Ryan Dewhurst from Spanish cyber-security firm Previdian.
The entry level to the affected freezer software program merchandise was not tough to take advantage of as they have been poorly protected, with identified assault strategies already floating round on-line.
However specialists like Dewhurst say the hacker or hackers needed to collect the details about the gadgets’ public IP addresses to create a goal listing then take time to plan which strategies to make use of and when to execute them.
“Given the reported timing of when the gadgets had their temperatures elevated, which appears to have been in a single day for max harm – that is additional proof that the assault was deliberate and co-ordinated,” he mentioned.
One other cyber agency which has deployed comparable honeypot tech to lure the hackers into revealing their techniques is Strathclyde-based Lupovis.
It had honeypots which seemed to be positioned all over the world, and began seeing exercise 10 days earlier than the second wave of cyber-attacks.
Intriguingly, the staff noticed hackers scanning and probing their faux freezer websites solely in Europe.
“We noticed none of our honeypots in locations like Africa or South America focused in any respect,” mentioned Lupovis founder Dr Xavier Bellekens.
“Even pots in Ukraine have been left alone.”